Score-Based Security Monitoring
for Splunk
Patronus SIEM helps security teams detect, investigate, and respond to threats faster with risk-scored incidents, MITRE ATT&CK mapping, and unified investigation workflows — all inside Splunk.
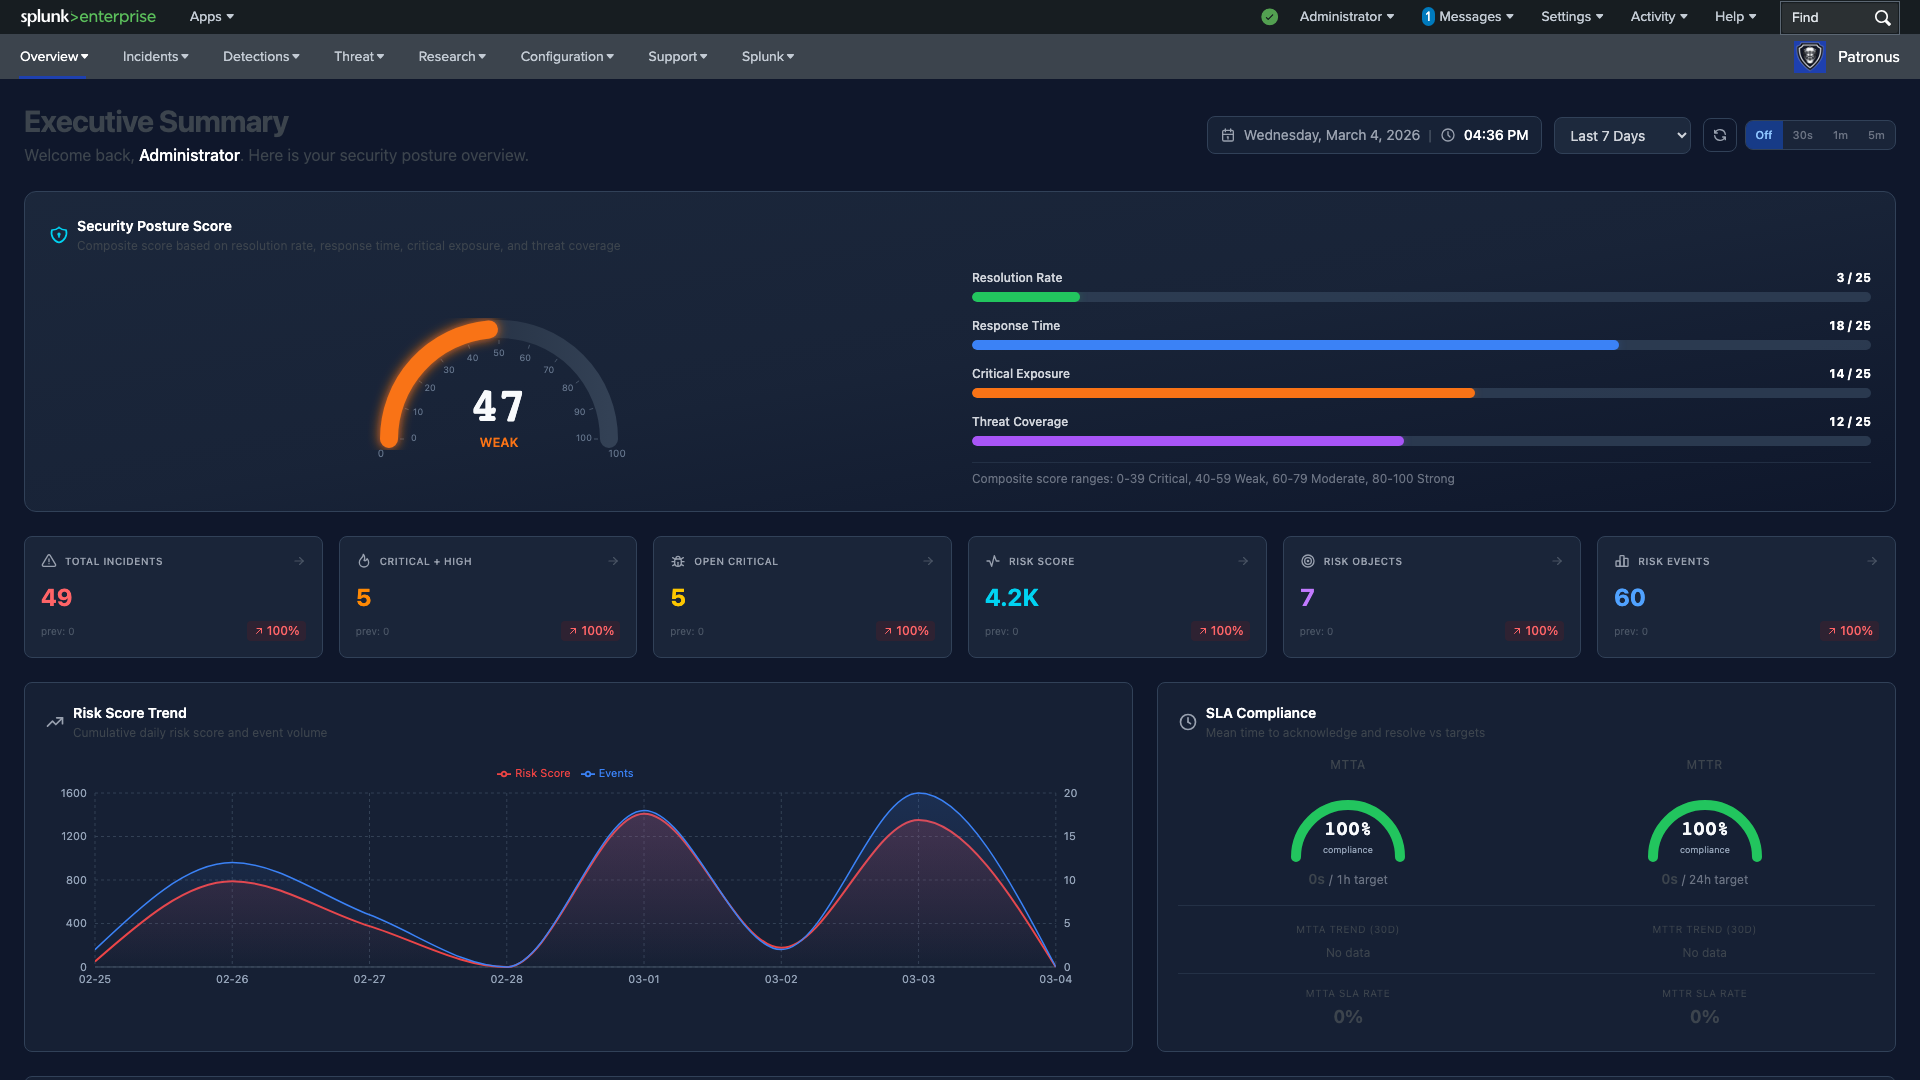
Executive Summary — real-time threat overview with global activity map, risk trends, and incident metrics
The Problem with Traditional SIEM
Security teams face these challenges every day.
Without Patronus
- Hours spent clearing noisy alerts instead of addressing real problems
- Bouncing between views trying to isolate root cause events
- Struggling to build event timelines that tell a coherent story
- Each alert treated as isolated, missing the bigger picture
With Patronus
- Risk scores aggregate low-signal events into high-confidence incidents
- Unified investigation view with correlated event timelines
- Many events build one incident — not one alert per event
- Dramatically less time on false positives and lifecycle management
What Matters Most
Time is the most crucial asset for a security team.
Time to Detection
Risk scores surface real threats from noisy data so your team knows what's happening as it happens.
Time to Investigation
Correlated timelines and deep-dive views let analysts trace an incident back to its root events in one place.
Time to Remediate
Incident management, SOC assignment, and immutable notes keep your response organized and audit-ready.
See It in Action
A few views from the Patronus SIEM Splunk app.
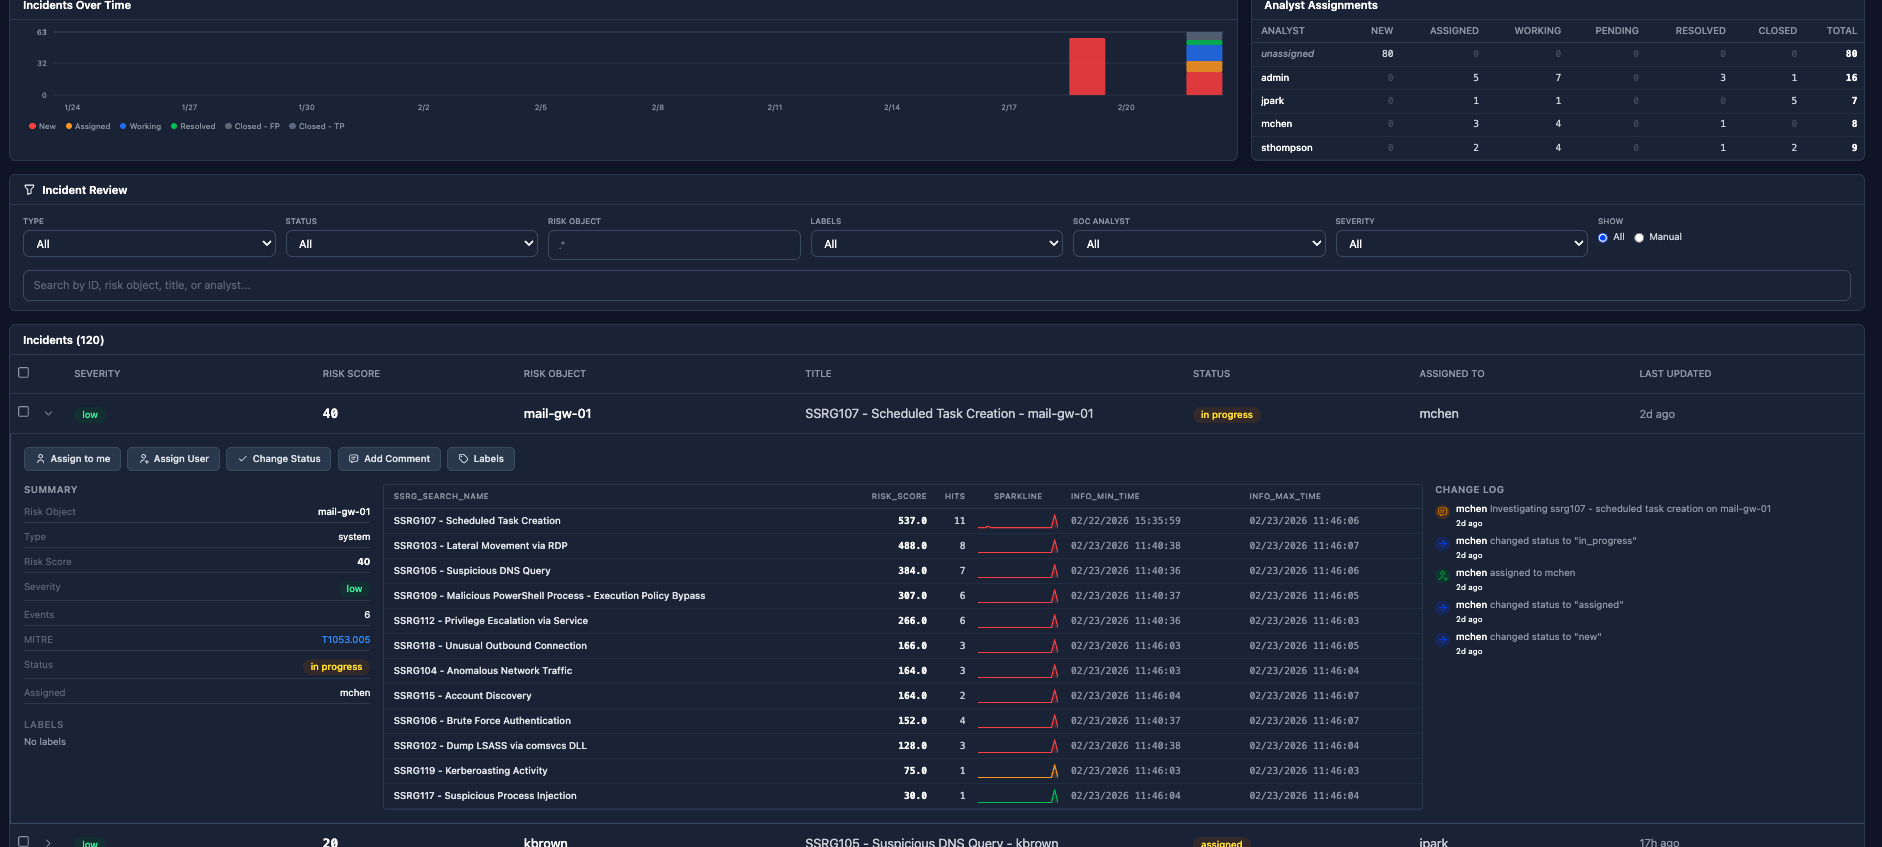
Incident Review
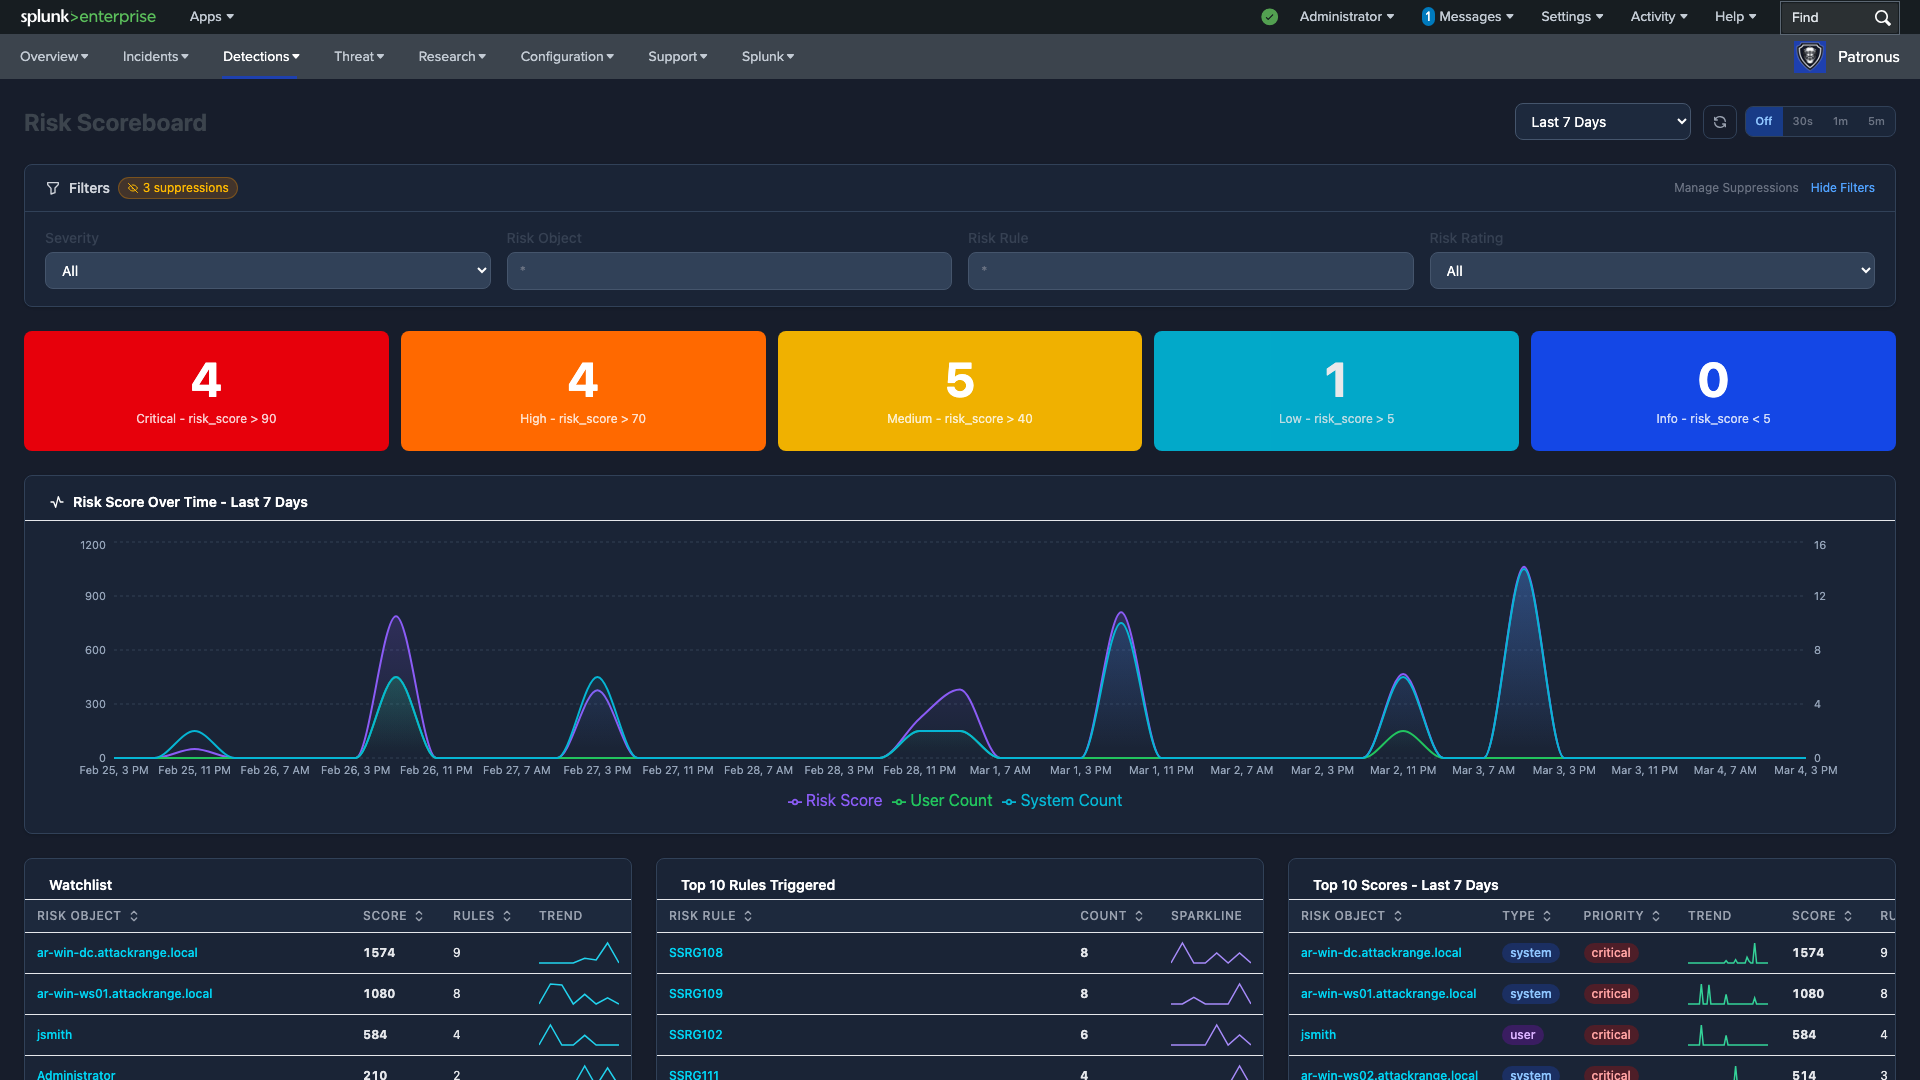
Risk Scoreboard
Built for Splunk Security Teams
Everything you need for detection, investigation, and response — natively inside Splunk.
Score-Based Incidents
Aggregate risk from many detections into high-confidence incidents instead of chasing individual alerts.
MITRE ATT&CK Mapping
Visualize detection coverage across the MITRE ATT&CK framework with an interactive technique matrix.
Threat Intelligence
Automated feed ingestion for IPs, domains, and file hashes with activity correlation against known indicators.
Incident Management
Full lifecycle tracking with status management, SOC assignment, inline commenting, and immutable audit trails.
Asset & Identity Research
Deep-dive into any asset or identity with correlated risk timelines and multi-source lookup enrichment.
Executive Dashboard
High-level KPIs, trend indicators, and incident summaries designed for team leads and management.
Ready to get started?
Check out the documentation to get Patronus SIEM installed and configured in your Splunk environment.