Features
Everything Patronus SIEM provides to help your security team detect, investigate, and respond to threats inside Splunk.
Score-Based Incident Generation
A basic scoring system applies a level of risk to all detections. As scores accumulate, they become compelling — eventually generating an incident once a prescribed threshold is exceeded.
Many events generate an incident and a timeline, rather than every incident representing a single event. This approach significantly reduces time spent on lifecycle management and chasing false positives.
- Configurable risk thresholds per environment
- Cross-layer risk aggregation for higher-confidence incidents
- Noise reduction — focus on aggregate scores, not individual alerts
- Severity cards, sparklines, and watchlist tracking on the Scoreboard
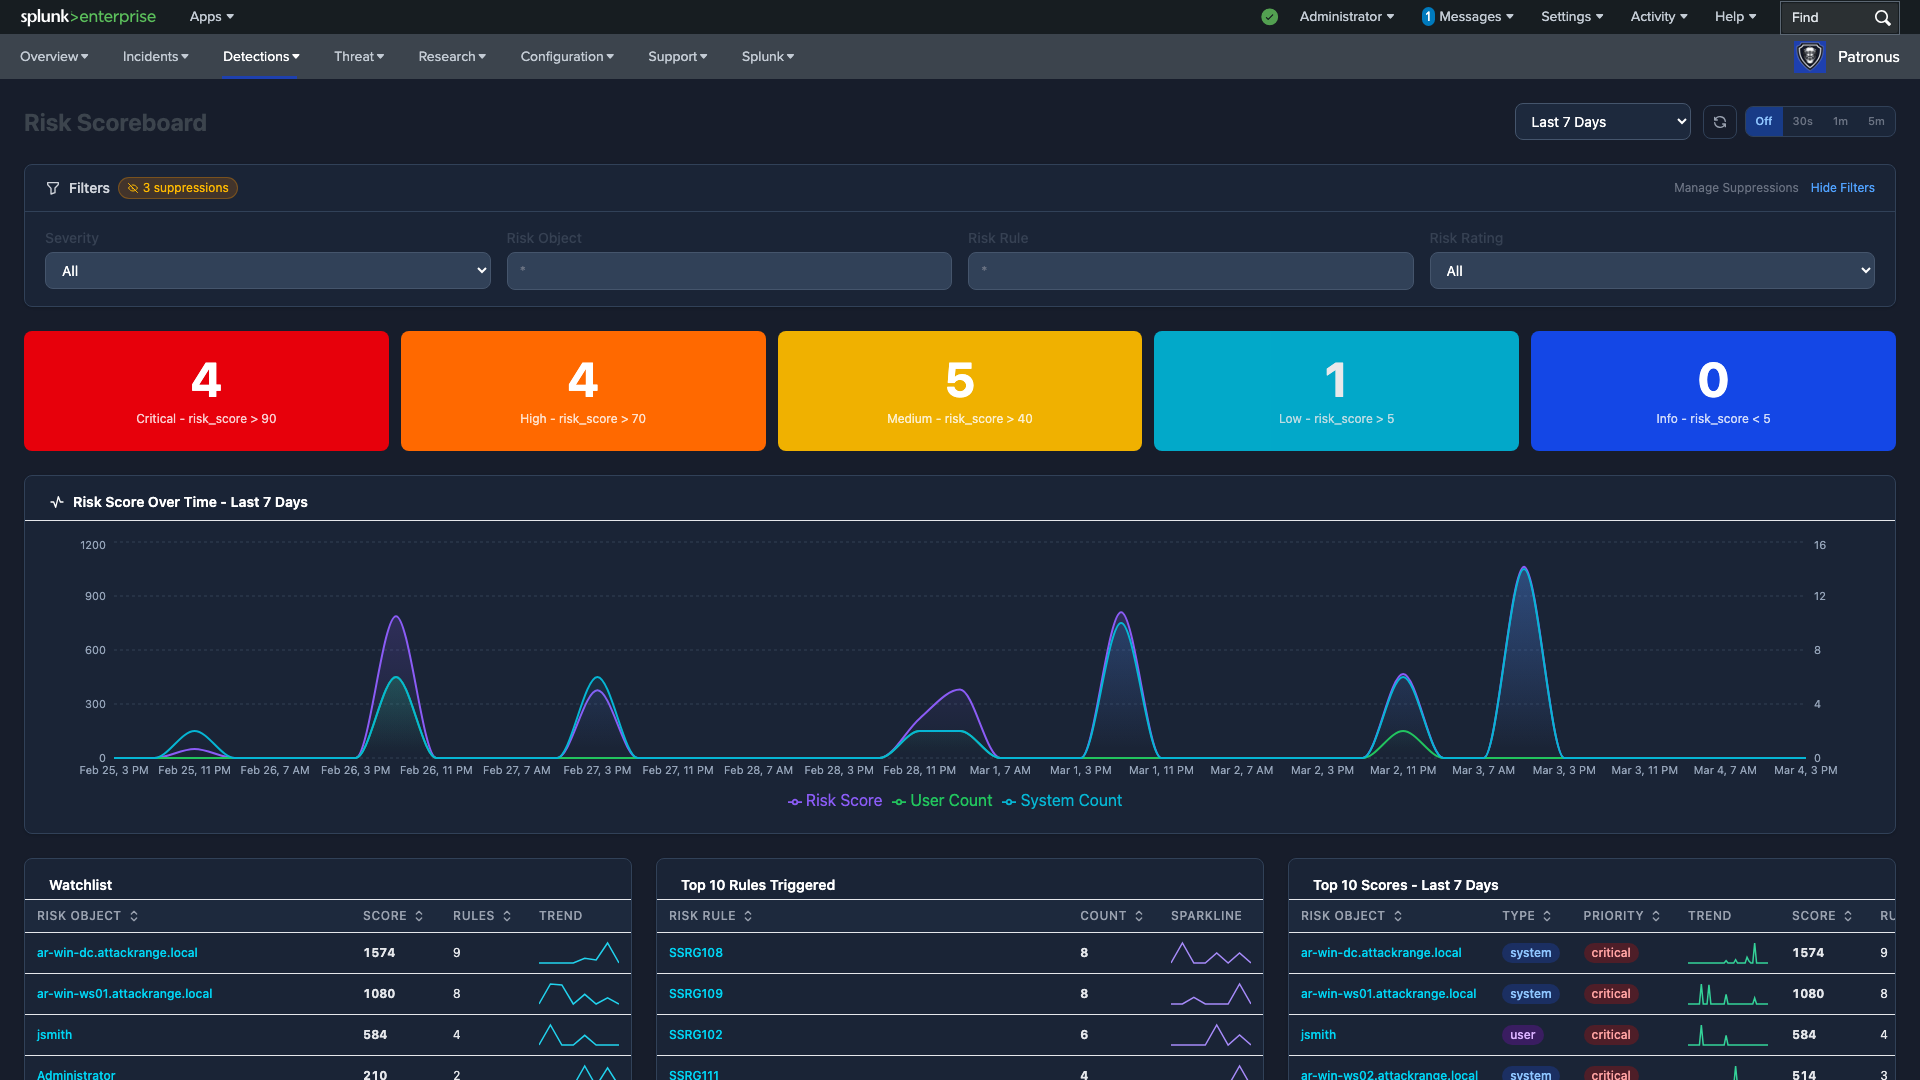
Risk Scoreboard — severity breakdown, risk trends, watchlist with sparklines, and top scoring entities
Incident Management
Full lifecycle management with status pipeline, SOC analyst assignment, inline commenting, workload tracking, and SLA compliance monitoring. Keep your security operations organized and accountable.
- Visual status pipeline: New, Assigned, Working, Pending, Resolved, Closed
- Analyst assignment with workload matrix and performance tracking
- SLA compliance gauges with MTTA and MTTR tracking
- Bulk export for compliance and reporting
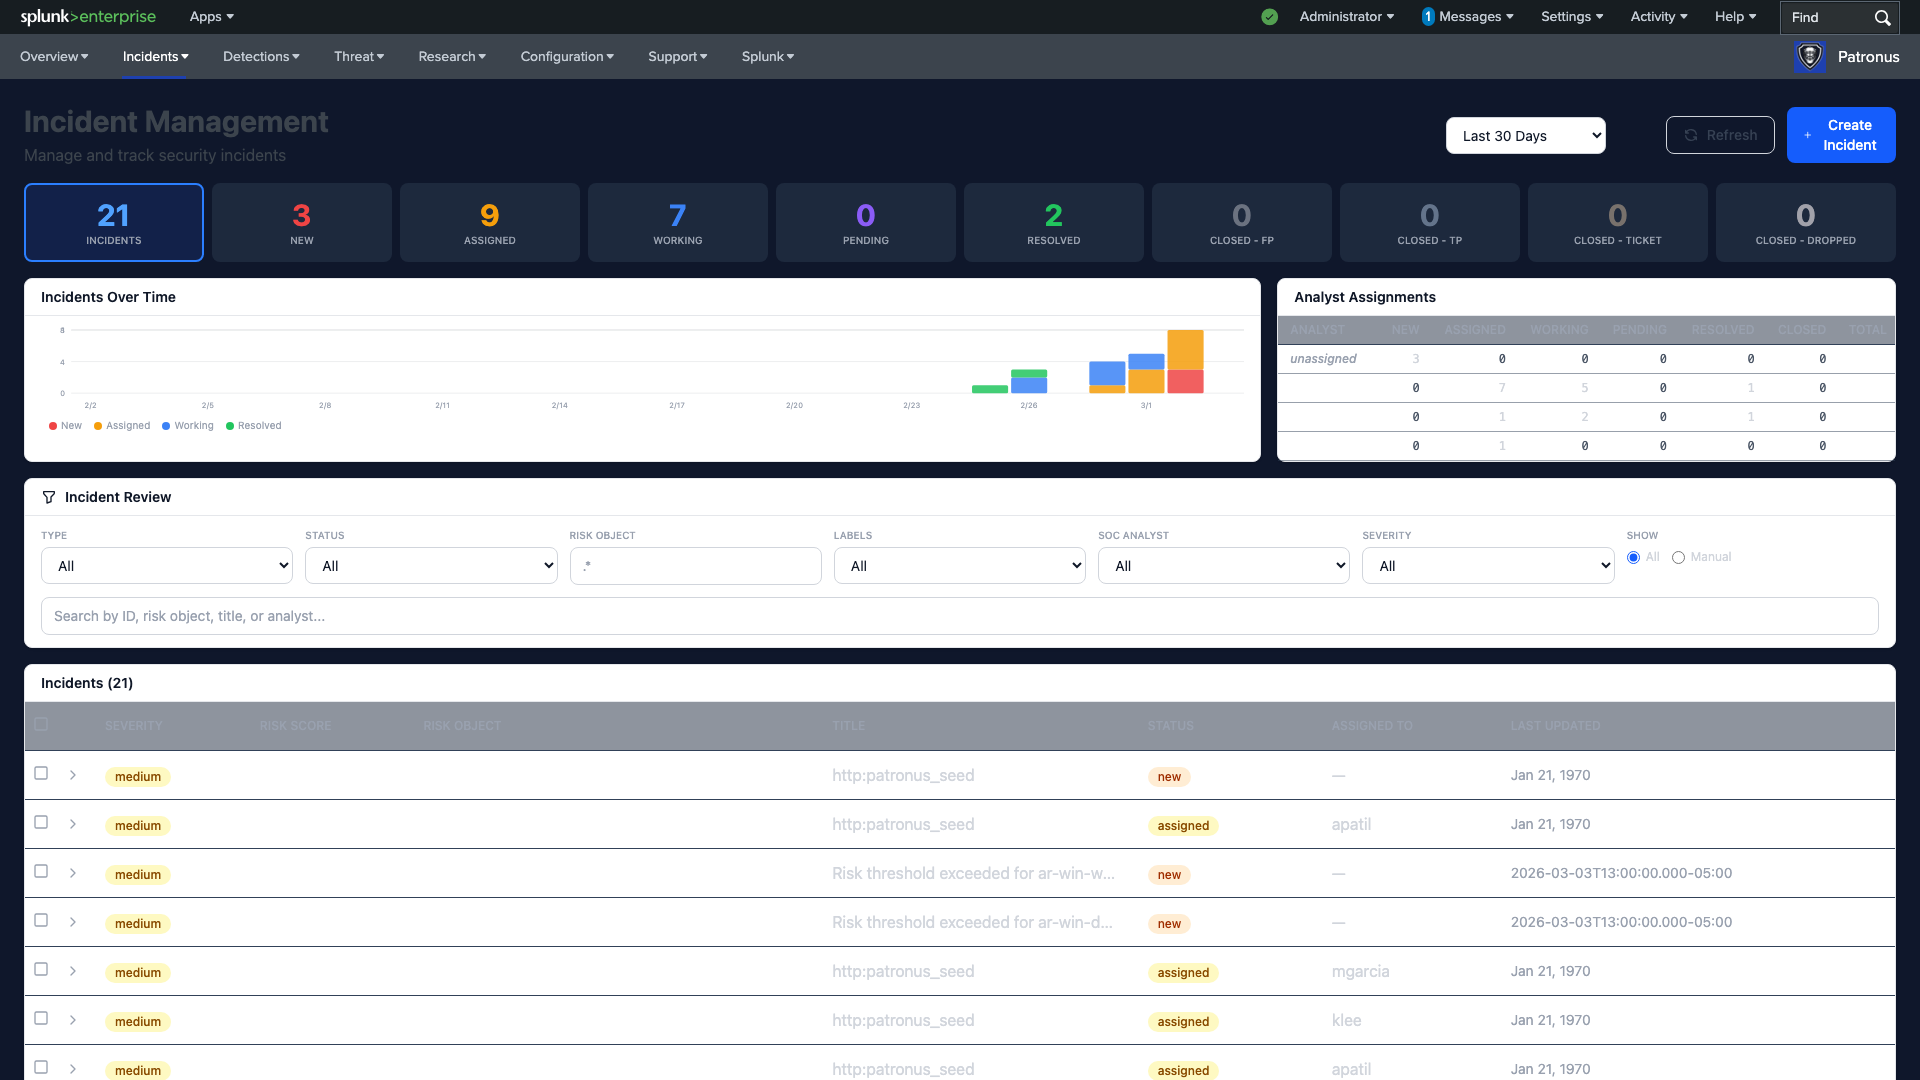
Incident Management — status pipeline, analyst workload matrix, and filterable incident table
Hunt Library
Browse, manage, and control your entire detection catalog from a single view. Toggle detections on/off, run searches on demand, and map everything to MITRE ATT&CK techniques with an inline editor.
- Enable/disable detections with one click
- Run Now dispatch — works even on disabled searches
- Inline MITRE technique editor with automatic tactic inference
- MITRE ATT&CK coverage matrix with tactic-level statistics
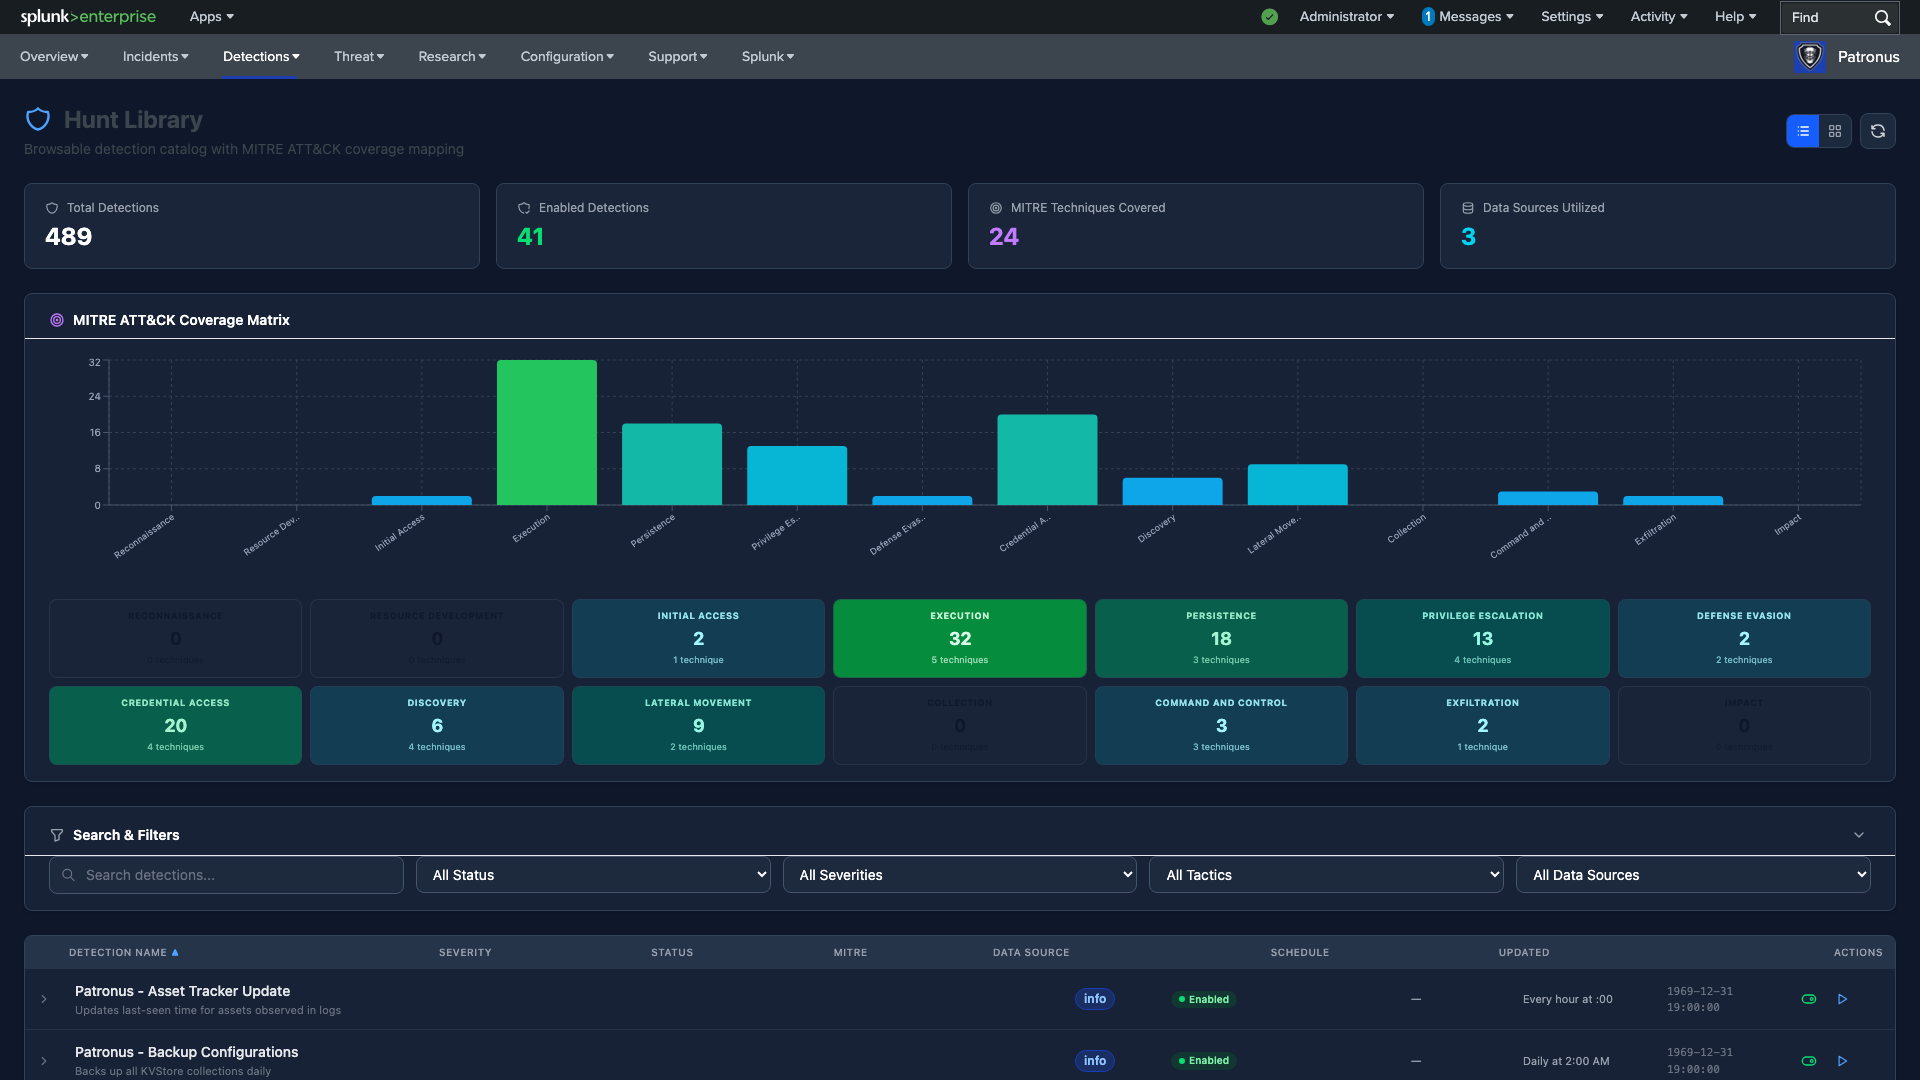
Hunt Library — detection catalog with MITRE ATT&CK coverage mapping and operational controls
MITRE ATT&CK Mapping
Visualize your detection coverage against the MITRE ATT&CK framework with three modes: available searches, enabled searches, and triggered events. Identify coverage gaps and prioritize new detection development.
- Full Enterprise Matrix with heatmap coverage intensity
- Three modes: Available, Enabled, and Triggered Events
- Click any technique to see contributing detection rules
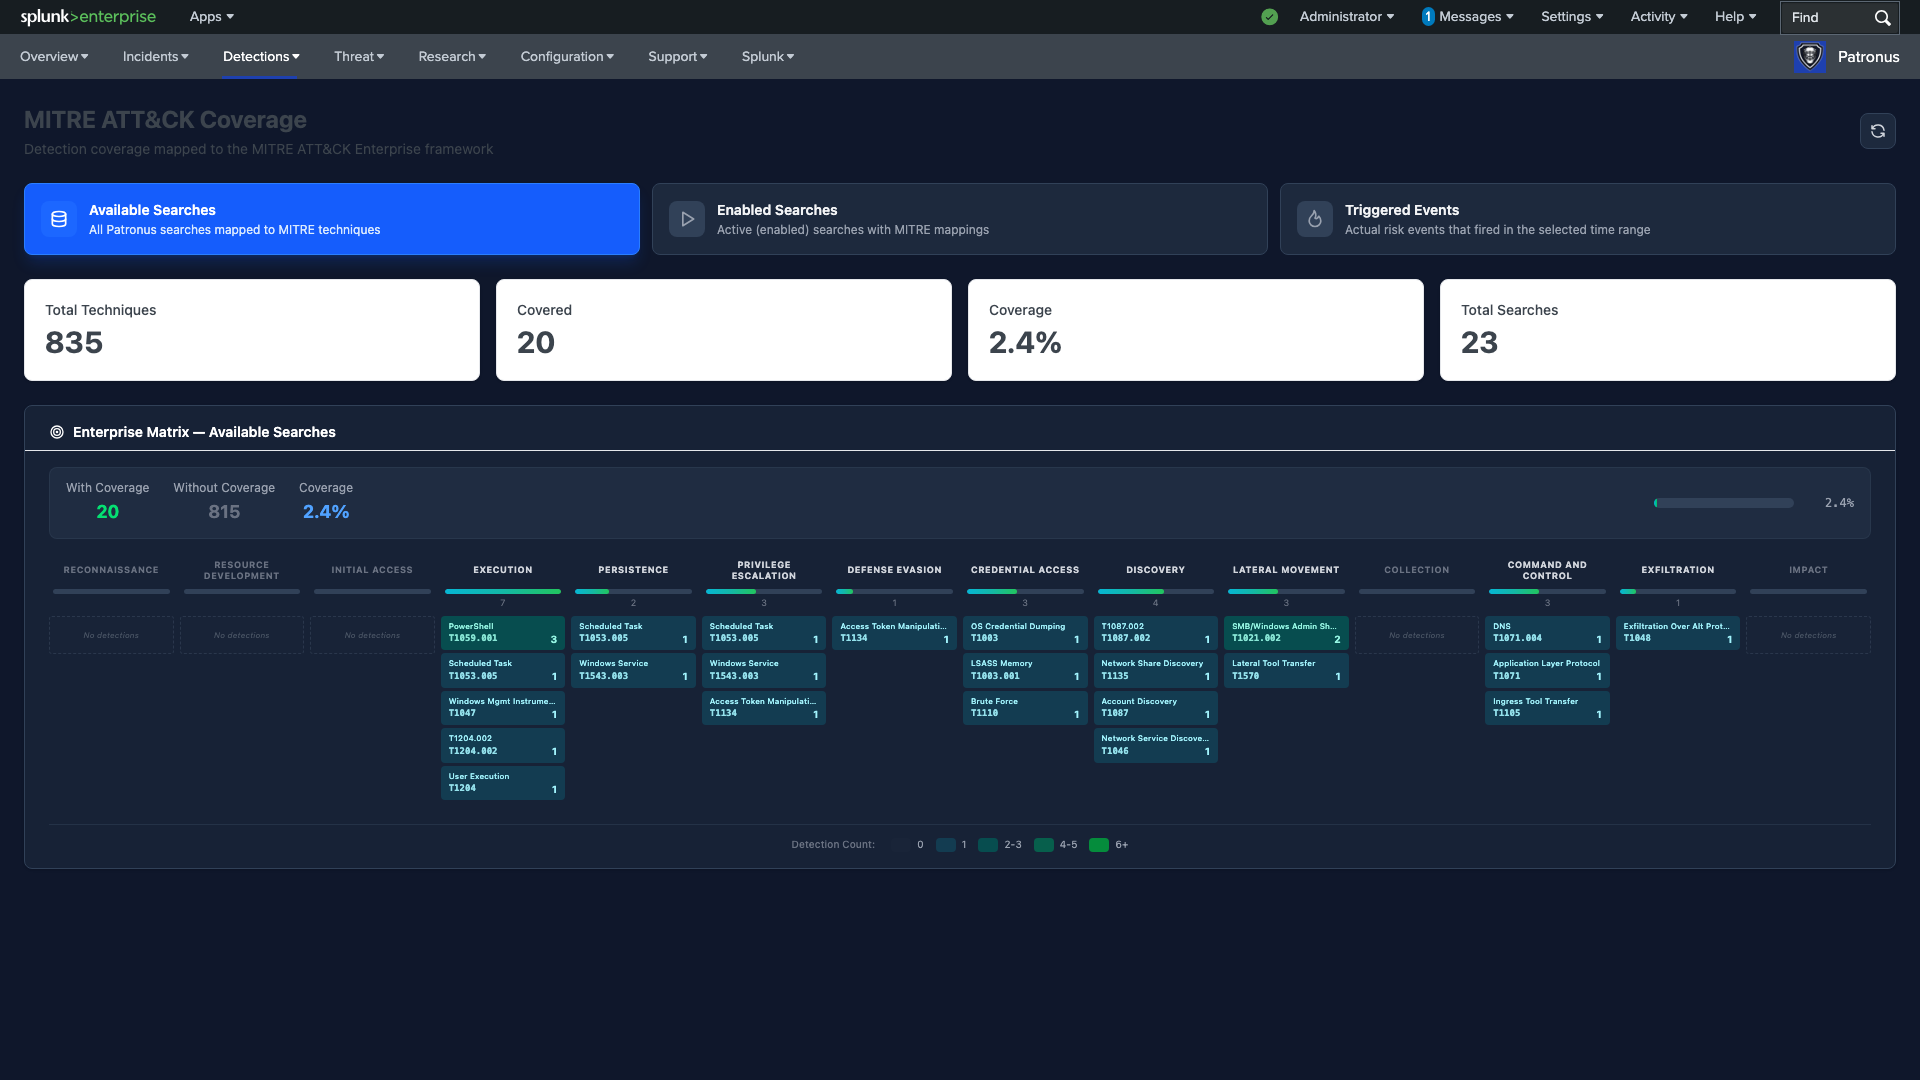
MITRE ATT&CK Enterprise Matrix — technique-level coverage with contributing rule detail
Threat Intelligence
Monitor threat indicators with feed health tracking, real-time correlation, and a dedicated Threat Inspector for investigating indicators of compromise against your environment's activity.
- Feed health dashboard with staleness tracking (Fresh/Aging/Stale)
- IP, domain, and file hash (MD5, SHA1, SHA256) indicators
- Threat Inspector for IOC investigation with known threats sidebar
- Auto-refresh with configurable intervals (30s, 1m, 5m)
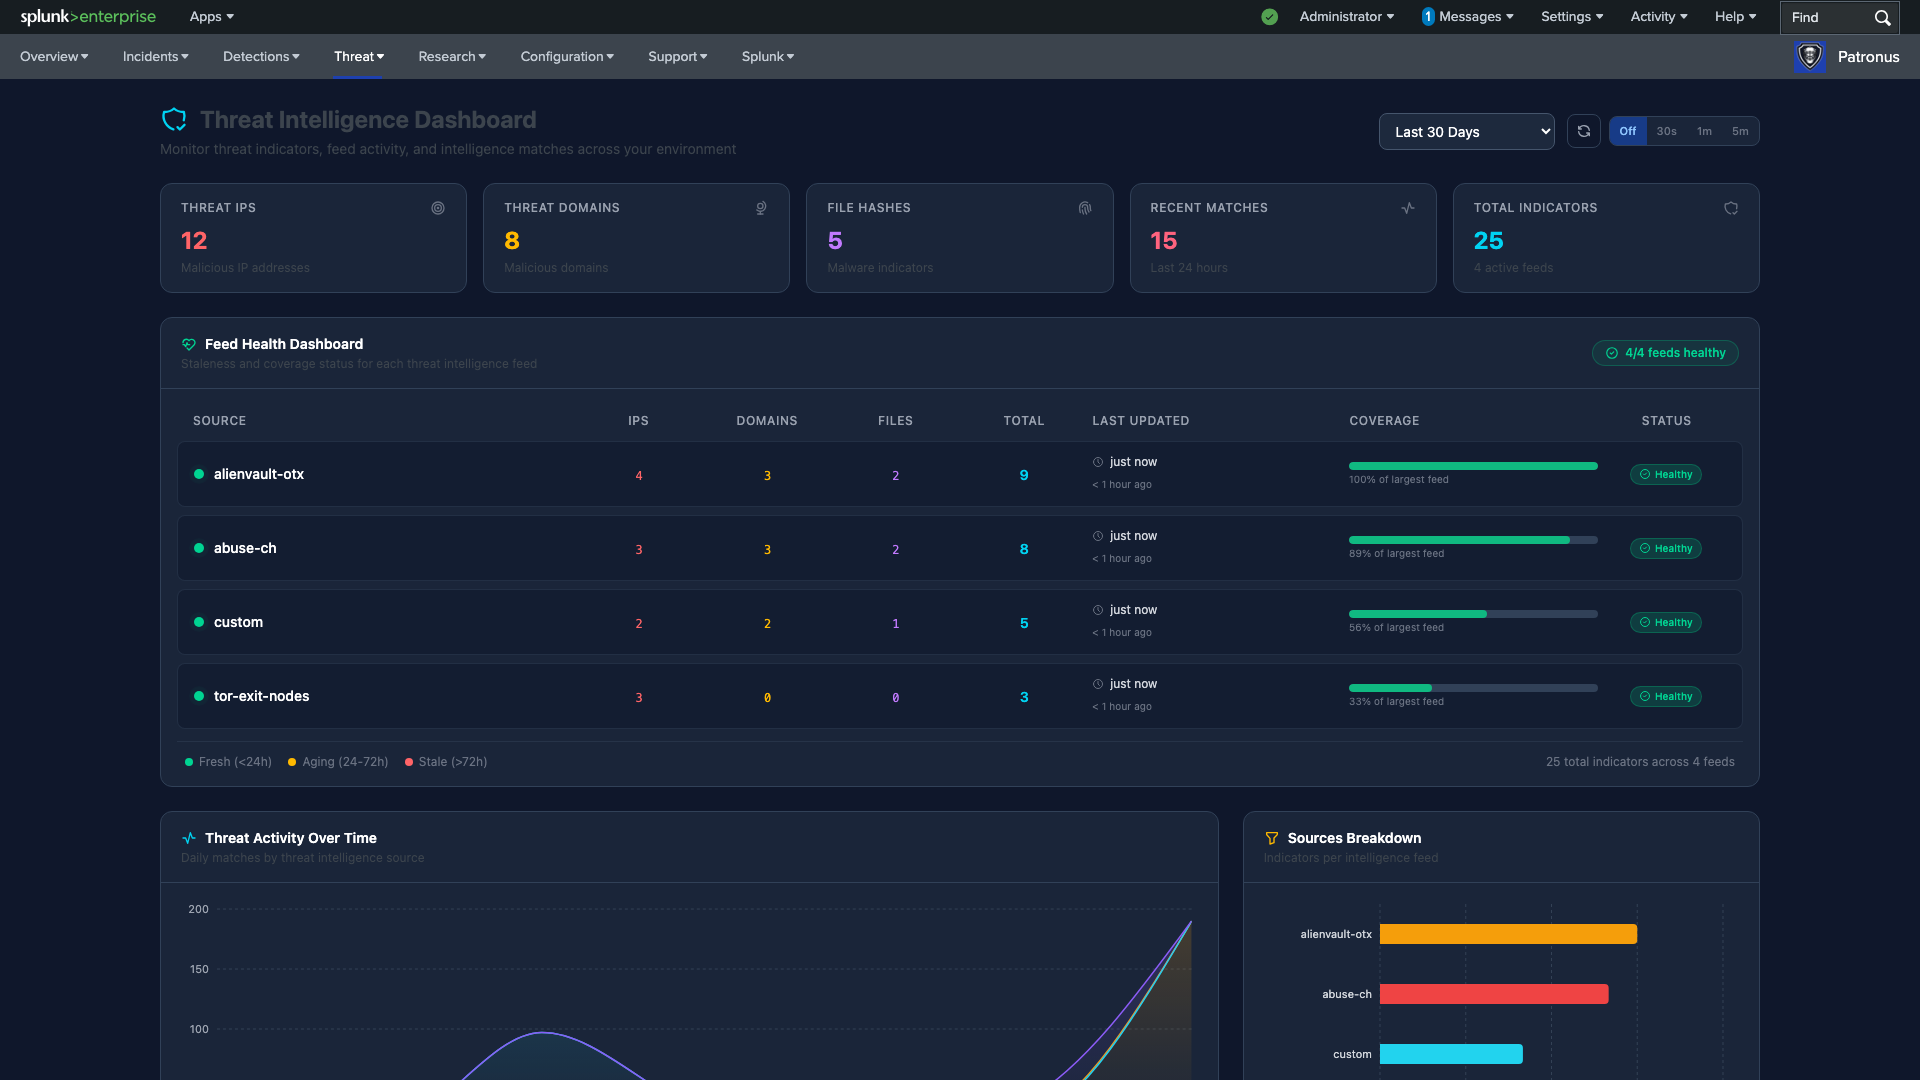
Threat Intelligence Dashboard — feed health monitoring, indicator counts, and activity trends
Asset & Identity Research
Deep-dive into any asset or identity with CIM data model swimlane visualizations, enriched metadata, combined activity timelines, and linked investigation views. Trace activity back to the device or user involved.
- CIM data model swimlane visualization (Auth, Endpoint, Network, Web, IDS)
- Enriched metadata from asset and identity lookups
- Interactive network relationship map with Sankey visualization
- Vulnerability tracking with CVSS scoring and age analysis
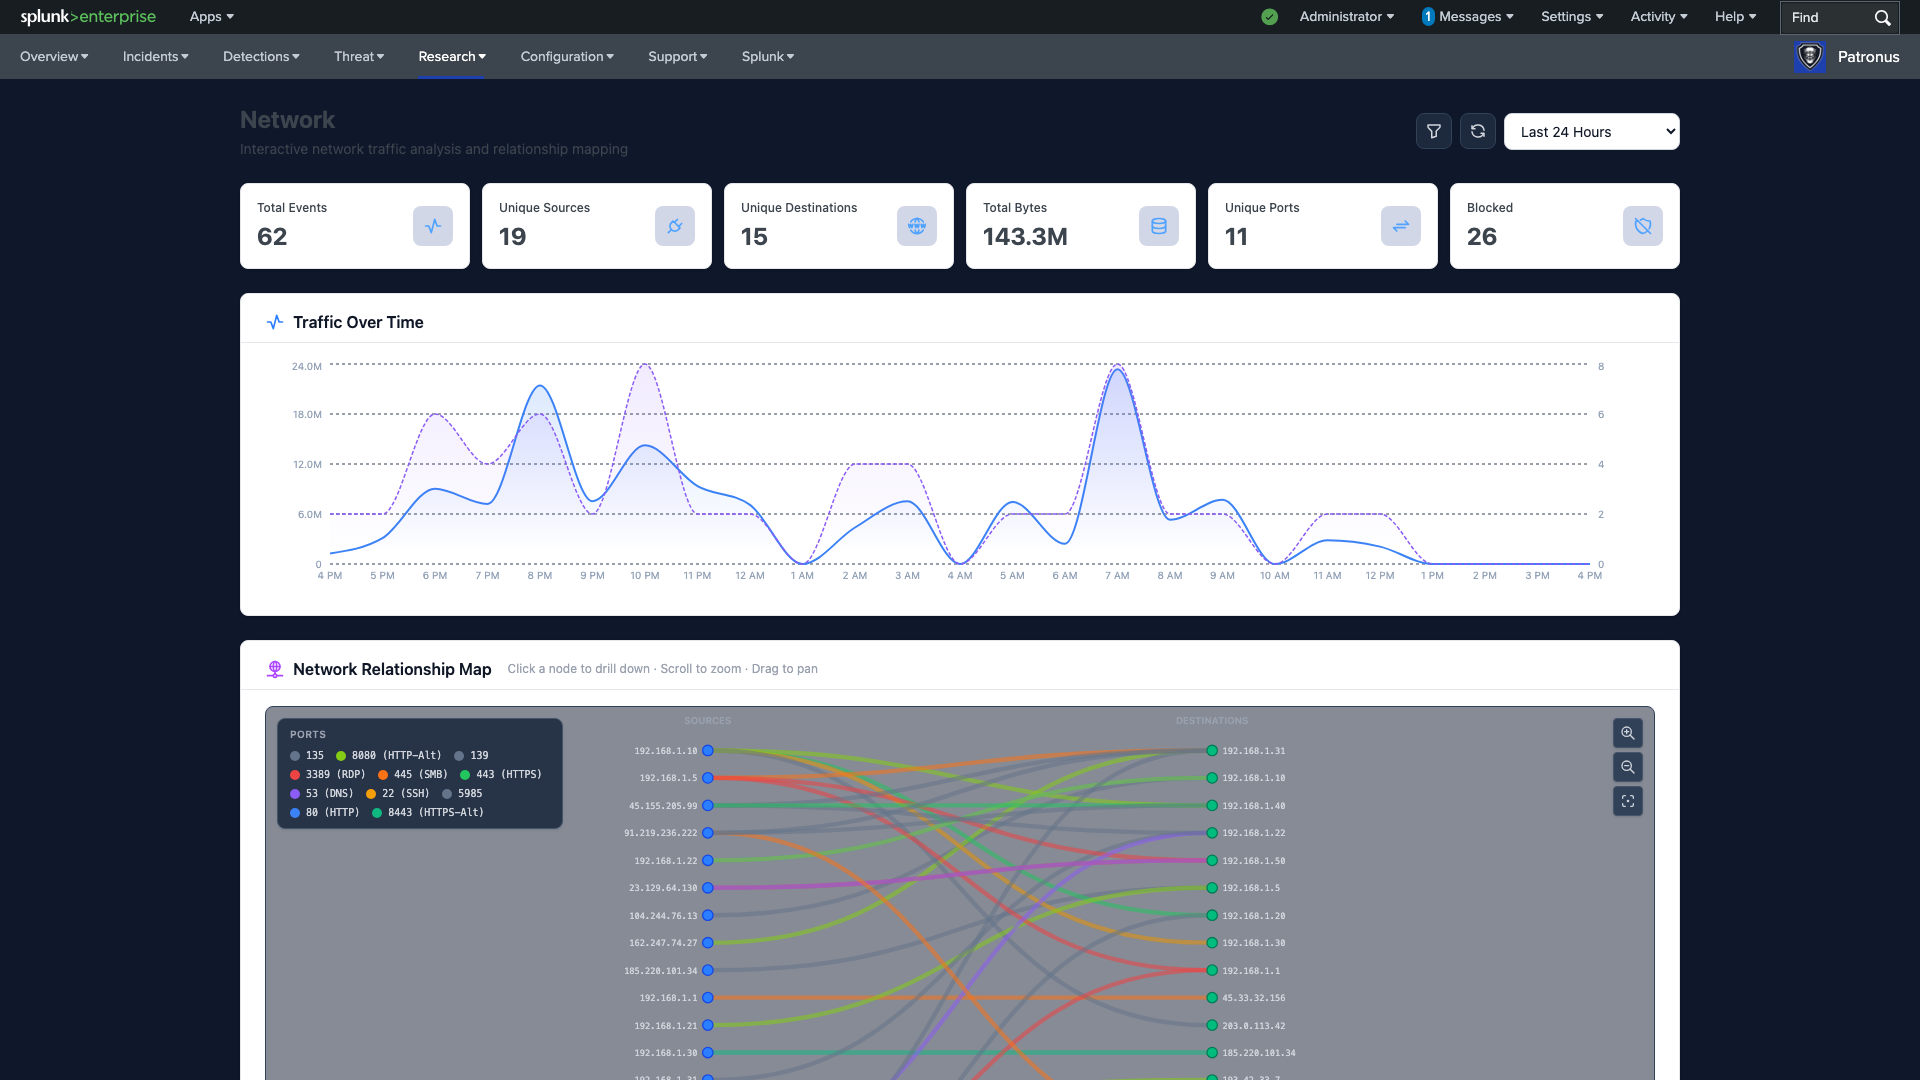
Network Analysis — traffic KPIs, timeline, and interactive relationship map with port/protocol color coding
Shift Handoff
Generate comprehensive end-of-shift reports for smooth SOC analyst transitions. Track what happened during the shift, what needs attention, and leave notes for the incoming team.
- Configurable shift periods (8h, 12h, 24h)
- Persistent shift notes with timestamps and author tracking
- Print-ready report generation
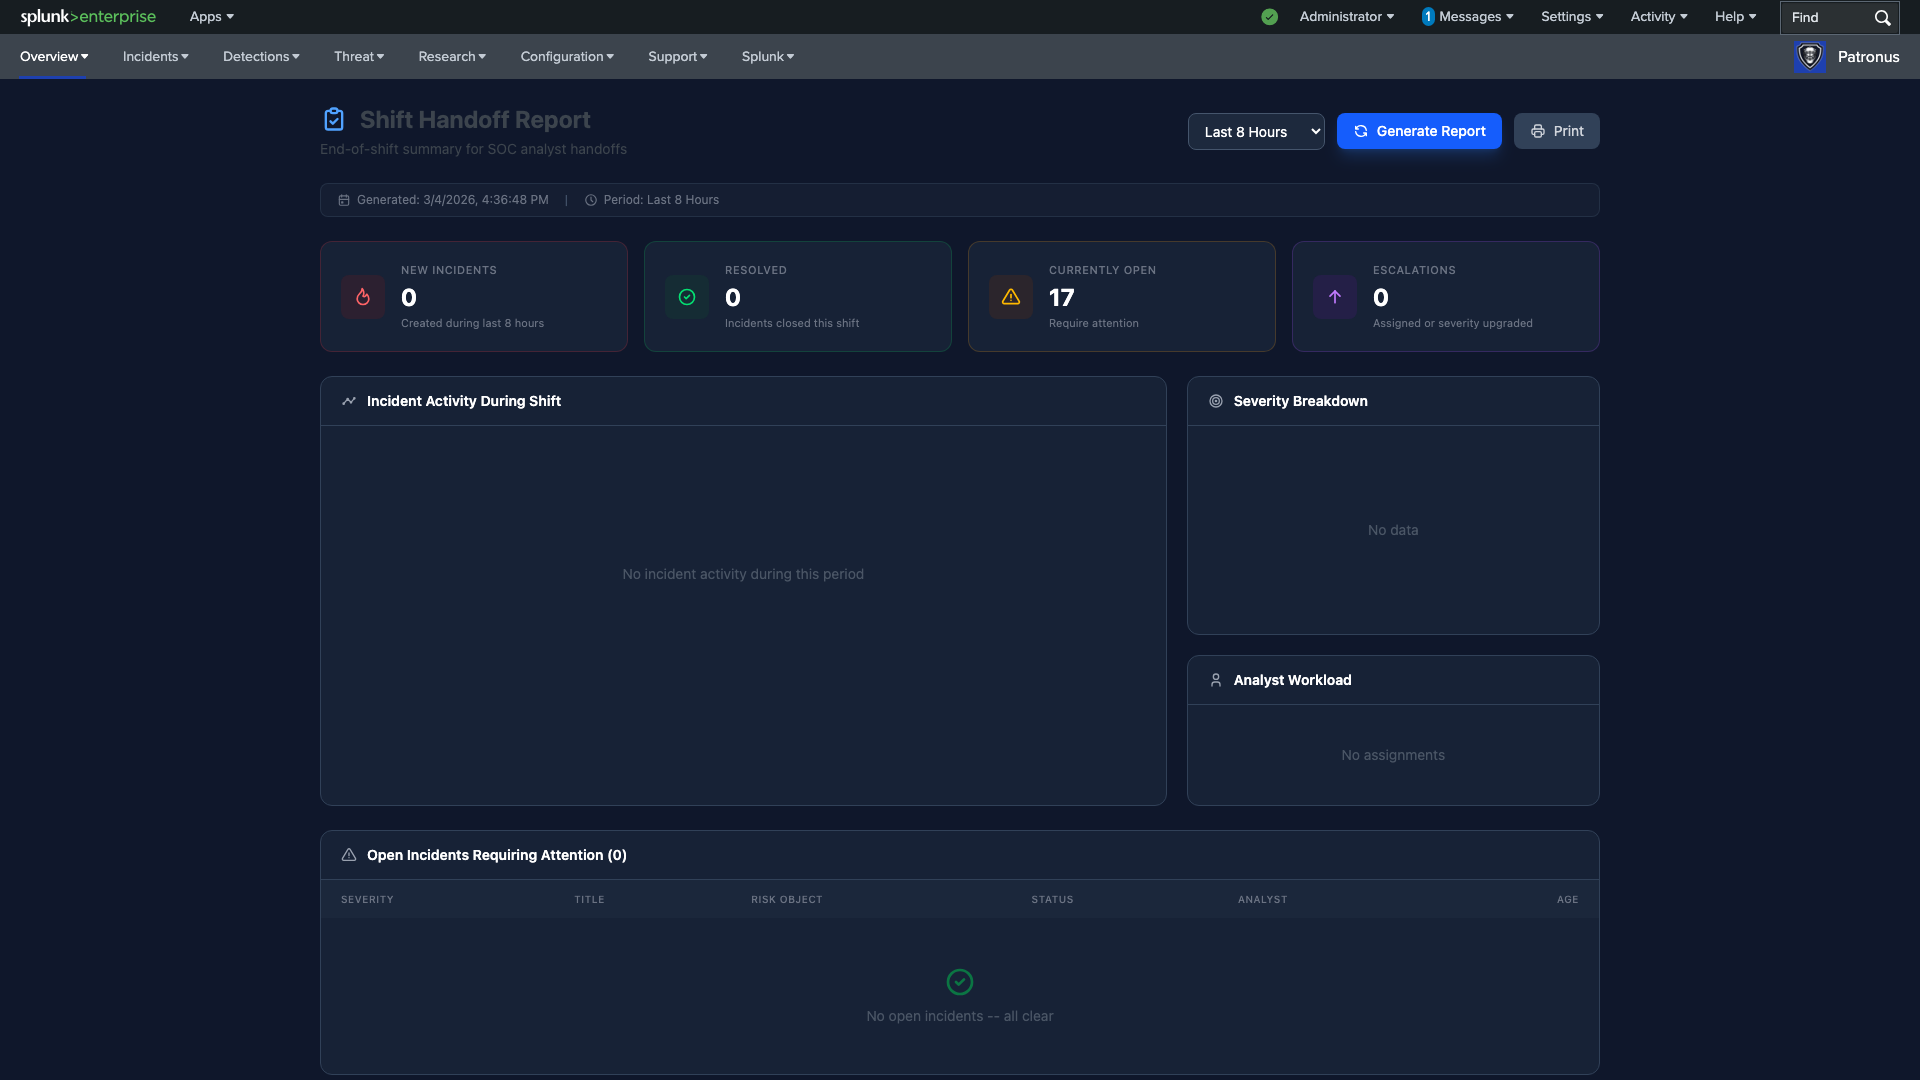
Shift Handoff — incident summary, analyst workload, open items, and persistent notes
Fully Configurable
Tailor Patronus SIEM to your environment with comprehensive configuration management — all settings in one unified tabbed interface.
Suppression Filters
Suppress known false positives scoped by rule, field, and value with expiration support.
SOC Analysts
Manage analyst roster for incident assignment and workload tracking.
Asset Management
CRUD management for asset inventory with enrichment for deep-dive views.
Identity Management
CRUD management for user identities with multi-source enrichment.
Corporate Subnets
Define internal networks in CIDR notation for traffic classification.
Watchlist
Track high-priority risk objects with real-time score monitoring.
Threat Feeds
Manage automated and custom threat intelligence sources with health monitoring.
SLA Targets
Configure MTTA and MTTR targets for SLA compliance tracking.
Get started with Patronus SIEM
Follow our setup guide to install and configure Patronus in your Splunk environment.